Introducing Trust Spotlight by Wolfia, a series featuring the people behind every security review, every policy, and every customer trust conversation. They’re often behind the scenes, playing a huge role in keeping deals moving. We think they deserve a spotlight too.
We’re featuring security and GRC leaders we really admire, sharing their real stories and lessons for the rest of us to learn from.
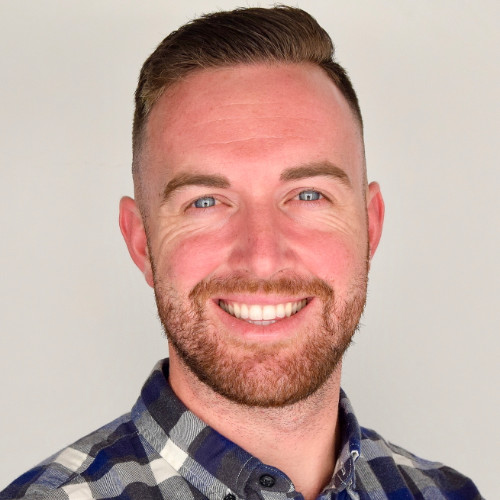
Our very first is Jon Zayicek, CISSP, Solutions Architect, Customer Trust at Decagon. He has 20+ years in this space, from the Navy and Marine Corps to securing AI agents.
How did you get into security?
My journey began in 2003, as a network administrator supporting the federal government on one of the largest networks ever built at the time, serving the Navy and Marine Corps. I was picked to help stand up a cybersecurity inspection team whose mission spanned the entire Department of Defense. That was the turning point of my career, and it laid the foundation for everything I’ve done in security since.
What do most people get wrong about security reviews?
The checkbox mentality. The goal quietly shifts from ‘Is this environment secure for our use case?’ to ‘Fill out the questionnaire, attach the SOC 2, get approved.’ People optimize for answering the questionnaire, not for improving the control environment. A framework can show a control exists on paper; it doesn’t show the control actually works against real threats. Compliance proves design; attackers test effectiveness.
What’s something Wolfia does that you haven’t seen from other tools?
It’s designed to stop when it should stop. If Wolfia can’t tie an answer back to something you’ve actually documented, it doesn’t force one, it kicks the question to a person. That matters to me because the risk I worry about isn’t a blank cell on a questionnaire; it’s a confident answer to a customer that turns out not to be defensible. Most of these tools are built to fill in more of the form. I pay more attention to the ones that are explicit about what they won’t answer.
It connects questionnaires to where commitments are actually made. The interesting part isn’t answering questionnaires faster; it’s that the same approved source of truth gets used when reviewing contract language and other customer-facing commitments. That’s usually where the gaps appear: between what gets promised in a contract and what security has actually documented.