


The trust center is where customers can go and download documents. Like your compliance certifications, your policy documents, and everything after signing an NDA.
The procurement team on the other side wants to get documents. Instead of them emailing you and then getting the document, they just go and self serve.
Buyers get your documents without emailing you
It’s gonna be part of your procurement process whenever you’re touching any big customer. It’s the same question, but it’s like 50 times.
You can totally get a questionnaire, have to share evidence, and having the capability in the trust center is so much more helpful than having an AE talk to an SC, talk to a GRC person, and then travel all the way back. It just slows down.
Your customer can come in and just download documents easier without raising support tickets.
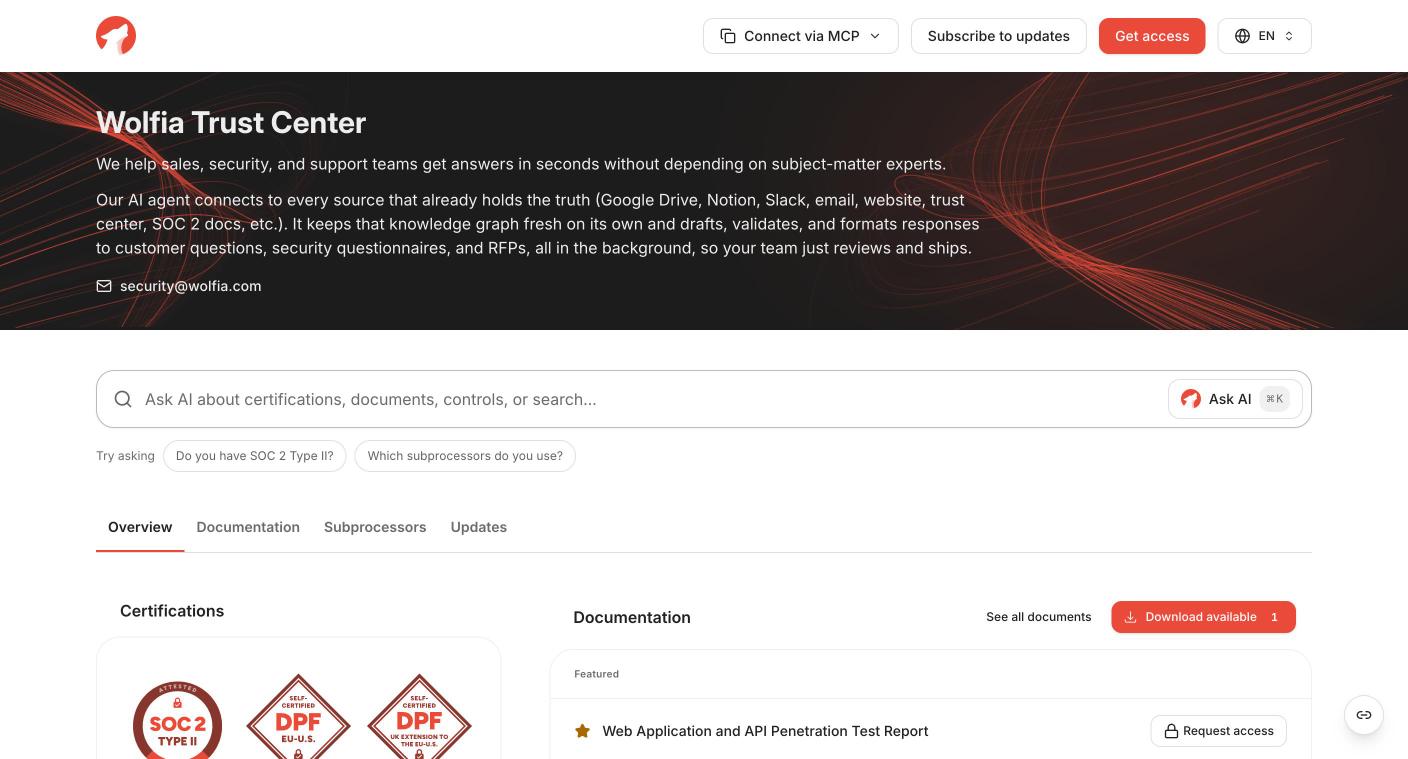
People love just coming in and clicking download all and then leaving. We try to not keep people in the trust center as much as possible because we just want them to get the job done and leave.
What should a trust center contain?
It all depends on who your customers are. We typically work with these companies that are selling into banks and health care.
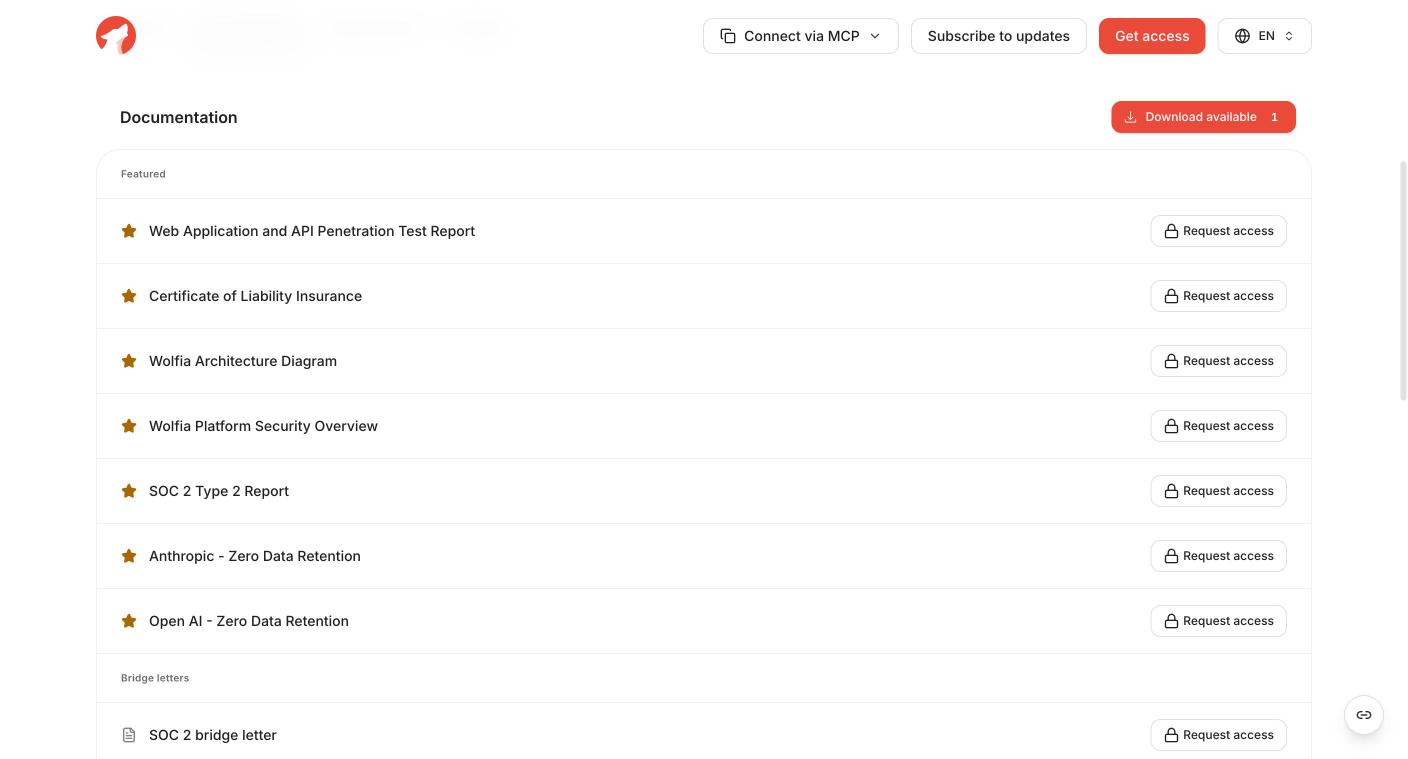
- Certifications and audit reports. All the certifications that you have. This is also configurable by business segment, so different business segments can have different certifications.
- A document library. You can upload your documentation and create different categories if you’d like. We also have expiry checking, so we can tell you the expiry for the pen test is coming through.
- Access requests and NDAs. For customers, we’re not gonna show an NDA. If they have an NDA currently signed, we’re also not gonna show them. If not, then they’ll need to sign an NDA.
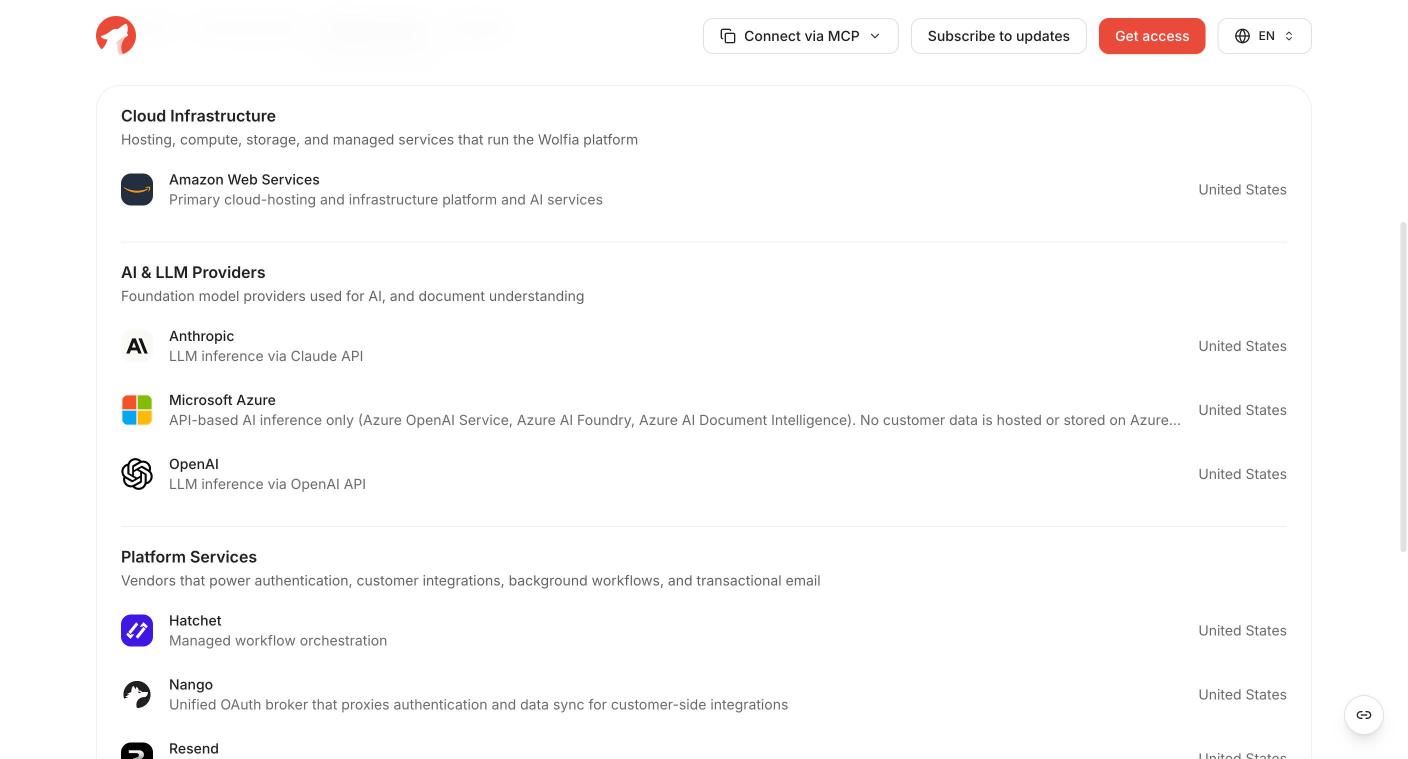
- A current subprocessor list. If you have a separate subprocessors page, you can tell Wolfia to sync data from that subprocessor page instead of having one person go and copy paste things to the trust center.
- Security controls and common answers. One of our customers realized 90% of all customers going into their trust center were downloading their CAIQ. So they spend extra effort keeping that up to date.
- Updates and a security contact. With updates, you can say something is visible to everyone. Imagine single customer impacted by a security incident. You don’t wanna blast that to everyone.
- Custom pages. For Juicebox, an AI company, their customers particularly care about what data they’re using for training, inference, and AI data governance.
Publish the overview, gate the evidence
If you make it publicly available, any third party management team can download the document. The second layer is if you want, you can get it behind an NDA.
| Information | Public or gated? | Why |
|---|---|---|
| Certifications and frameworks | Public | Buyers can check what you hold in seconds |
| Subprocessor list | Public | Customers need to know who handles their data |
| High-level security controls | Public | Shows your approach without exposing internals |
| Security contact and vulnerability reporting | Public | People need to know where to send things |
| SOC 2 report and pen test | Gated | Detail meant for approved viewers |
| Architecture diagrams and detailed policies | Gated, sometimes per customer | Too specific to publish |
If it’s a customer, don’t ask them an NDA. Give them access to the portal immediately. If it’s a hot deal, give them access instantly.
So there doesn’t need to be a human being sitting and approving access.
A security page explains, a trust center proves
You gotta understand it from a buyer perspective. What they wanna do when they go to a trust center is download your docs. They literally do not care about anything else.
| Type | What it does | What buyers get |
|---|---|---|
| Trust center | Holds your security information and the evidence behind it | Public information, restricted documents on request, an access record |
| Security page | Explains your approach to security | A high-level overview |
| Compliance page | Lists your certifications | Badges and framework names |
| Shared folder or emailed PDF | Sends files to one person | Only the files they were sent |
Make sure your marketing team is comfortable putting this out there. Your customer is going to interact with this in some way, shape, or form. The way you talk, you probably want that to be synonymous with your marketing page.
A trust center shortens questionnaires, it doesn’t replace them
A lot of our customers try to deflect questionnaires with trust center, doesn’t really work. If a bank wants a questionnaire answer, they’re going to send it to you and they’re going to want you to do it.
Whenever someone asks for an attachment, you can just point people to go to the Trust Center and download documents from there. The benefit there is you can track everything.
| Without a trust center | With a trust center | |
|---|---|---|
| Buyer’s first step | Emails sales for documents | Opens the trust center |
| Common questions | Answered again for every buyer | Published once |
| The questionnaire | Repeats things you’ve already shared | Focuses on what’s left |
| Document sharing | Attachments and shared folders | One library with access requests |
| Versions | Old copies keep circulating | Buyers see the current approved version |
| Who saw what | Buried in email threads | Recorded for every request |
There is good benefit to keeping the questionnaires and the trust center at the same place because you don’t want to contradict things and you want to keep everything in one place. We saw Amplitude go from a week long SLA for security questionnaires to a day.
“The sales team thinks it's magic. They send in a questionnaire and get responses back the same day.”
Garrett Close, Head of GRC at Amplitude
How to build a trust center in six steps
Trust center is the easiest. We can get something stood up within half a day if you just share the documents.
- Put it on your own domain. You can add your custom domain. Make it look exactly similar to your marketing website and make it look nice.
- Decide who gets in automatically. If a customer is coming through renewal and they want documentation, we can check that they’re an existing customer. We can just auto approve their request. You can also reject specific domain. So competitors, anyone that you don’t want to have access to.
- Upload the current versions. You can upload your documentation. We also have expiry checking. So we can tell you the expiry for the pen test is coming through. You might wanna upload that.
- Answer the questions you hear most often. Pull them from your last few questionnaires. Encryption and access control and incident response are usually at the top.
- Keep it current. When something changes, we’re gonna prompt you for an approval. We also generate an update automatically.
- Connect it to your questionnaire process. You almost want your knowledge base and your trust center to be in sync. That’s the reason why people keep it in one place.
That whole process, I would say probably give it 2 to 3 days where we might need to iterate back and forth.
See a live trust center
Any third-party risk management team that’s looking to purchase Wolfia and want to understand Wolfia security posture can come in and self-serve documentation.
What I’ve seen successful customers do is they’ll write up an onboarding document for their sales team. Whenever a prospect is at this stage, send this message to their security team. I think the third party risk management person wants to get their job done as fast as possible.
“In buyer conversations, I show the Wolfia Trust Center more than some of our product features.”
David Paffenholz, CEO of Juicebox